

4 MIN READ
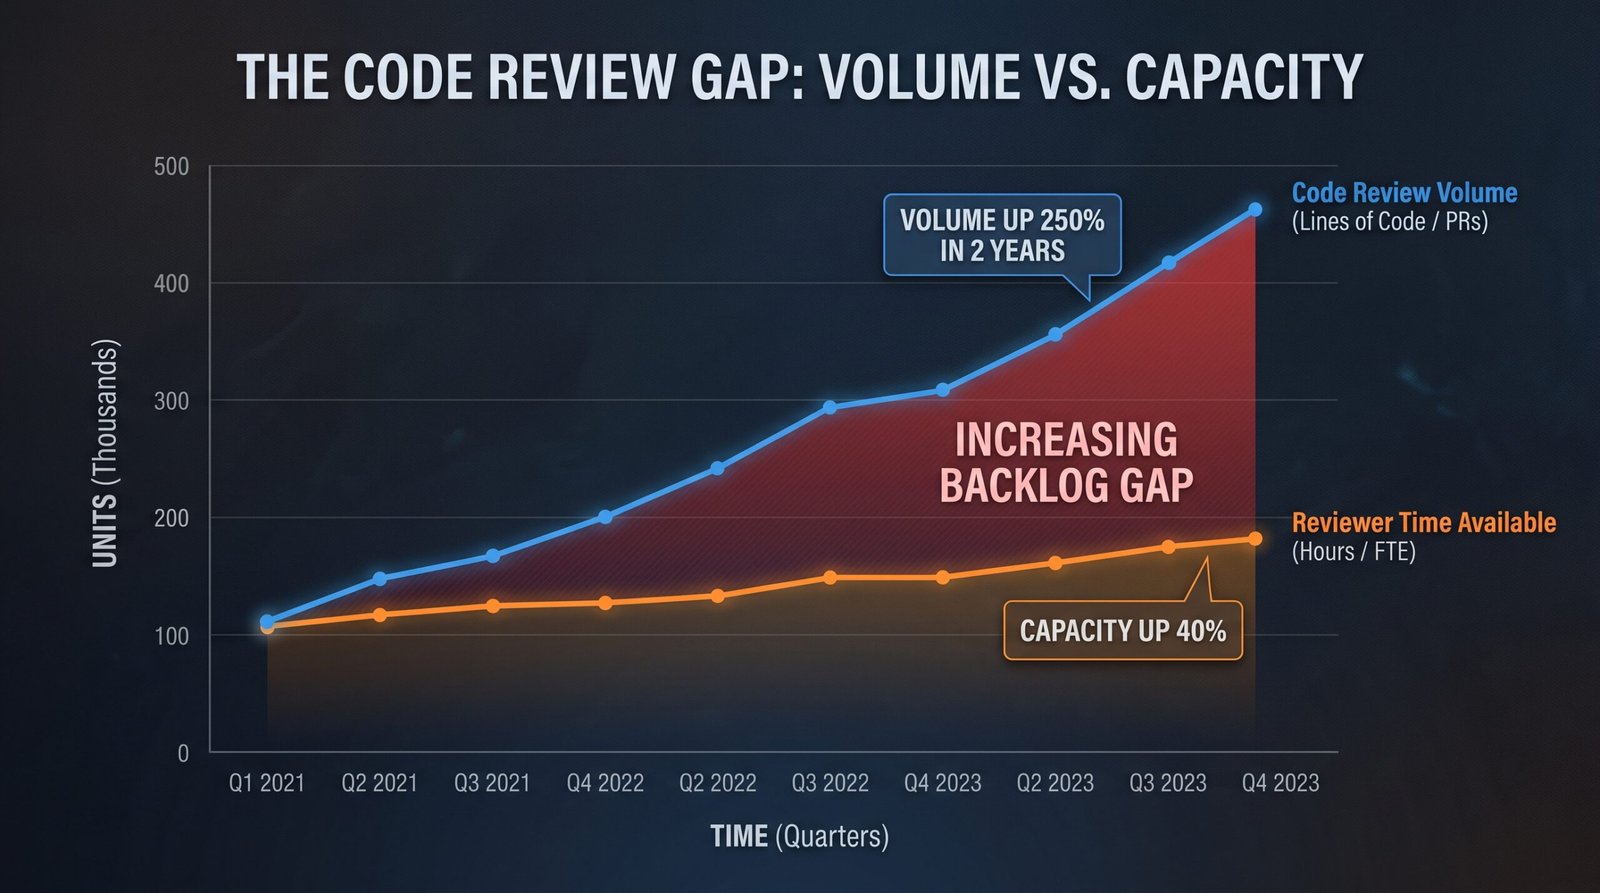
The code review process that worked at 5 engineers and 50 lines a day is the same one breaking at 50 engineers and 5000 lines a day. PRs sit for 3 days. Reviewers read 500 line diffs in 8 minutes. Bugs ship. Production pays the cost.
GitHub reported the median pull request review time at 4 hours in 2025, and the median pull request size at 247 lines. The engineering org that grew from 5 to 50 has 10x the volume and the same reviewer pool. The math stopped working around 2022. AI generated code has been accelerating the gap since 2024, and the org that has not changed the review process is the one whose defect escape rate is the line on the incident dashboard nobody wants to explain in the next retro.
What is breaking, in concrete terms
Three failure modes, each worse than the last. Volume first. A 5 person engineering org opening 5 PRs a day becomes a 50 person org opening 50 PRs a day, and the review capacity has not scaled with the headcount. The PR that waits 3 days for review is the PR where the author opens a new branch, the next PR ships first, and the context for the original change is gone by the time the reviewer picks it up. Size next. A 50 line PR becomes a 500 line PR the moment Copilot or Cursor generates the change in a single commit, which is most of the time in 2026. The human reviewer who has 8 minutes for a 500 line diff reads at the level of the whitespace, not the level of the logic, and the bug that lives in the third nested conditional ships because the reviewer never got past the imports. Cognitive load to round it out. Five PRs in the queue, a meeting in 30 minutes, the incident from yesterday still on the brain, the deploy that is happening now. The human reviewer who is context switching is the one who misses the bug, and the bug is what the next 2am page is going to be about.
What works in 2026
Three patterns, each one a real fix rather than a slogan. Small PR enforcement first. The CI pipeline blocks any pull request over 200 lines (GitHub branch protection, GitLab push rules, trunk based development), the engineer has to split the change into multiple PRs, the split adds review time but it also adds the test coverage, the design clarity, and the deployability that the single mega commit was missing. Most orgs that enforce the cap find their median PR size drops to around 80 lines within a quarter. AI assisted review next. GitHub Copilot for PRs, Cursor Bugbot, Greptile, Graphite Reviewer, and the dozen other competitors in the space all handle the mechanical half of the review. The syntax error, the style violation, the missing test, the obvious security smell (the hardcoded secret, the SQL string concat, the missing input validation) all get caught before the human reviewer opens the diff. The human reviewer handles the half that requires judgement. Domain reviewers to round it out. The org that has the designated reviewer for each domain (AppSec for the security PR, the data platform lead for the data PR, the platform org for the platform PR) gets the review by the person who actually understands the change. The generalist reviewer who has to context switch into every domain misses the bug, and the bug is what the next incident postmortem is going to spend an hour on.
What the engineering lead does on Monday
Three priorities, in this order. Set the 200 line PR limit in CI first. GitHub branch protection, GitLab push rules, Bitbucket pull request limits, the enforcement lives in the pipeline rather than in the engineering norms, because the engineering norms drift and the pipeline does not. Roll out AI assisted review next. Copilot for PRs is the default for most engineering orgs in 2026, Cursor Bugbot has been gaining share on the AI heavy codebases, and the rollout is a single repository admin setting plus a one line config file. Assign the domain reviewer rotation to round it out. Security PRs route to AppSec, data PRs route to the data platform lead, infrastructure PRs route to the platform lead, and the rotation spreads the load across the senior engineers in each domain. The metrics to watch: time to first review under 4 hours, PR size distribution with the median under 200 lines, and defect escape rate trending down over the next two quarters. The org that has all three is the one whose code review process finally scales.
The bottom line
200 line PR cap, AI assisted review, domain reviewer rotation. The engineering org that enforces all three is the one that catches the bug before the bug catches production.
Sources & Further Reading
All claims in this article are sourced from primary documentation, vendor advisories, and reputable security researchers.
Spotted an error? Email the editor. Corrections are issued with a visible correction note.
Editorial standards. Every article on humanrequired.org is reviewed by a human editor before publication. AI may assist with drafting or research; final editorial control is human. Read the full standards.


