8 MIN READ
Same tools, same techniques, same outputs. The hacker and the penetration tester use the same Nmap scans, the same Burp Suite workflows, the same exploit chains, and the same reporting templates. The difference is not in the craft. The difference is in two things: the motivation, and whether the system owner said yes. That is the whole field, and most of the arguments on the topic miss both points.
Worth saying out loud. The Computer Fraud and Abuse Act in the United States, the Computer Misuse Act in the United Kingdom, and the equivalent statutes in most jurisdictions draw the line at authorisation, not at skill. A penetration tester who runs an exploit without a signed rules of engagement document is a criminal, and a criminal who happens to be running an authorised assessment is still a criminal. The consent is the line. Everything else is colour.
What the hacker actually is in 2026
The modern threat actor landscape splits into four rough buckets, and the buckets overlap more than the marketing material suggests. State actors run for geopolitical goals, usually with patient access, usually in energy, finance, defence supply, and critical infrastructure. Criminal groups run for money, increasingly through the ransomware affiliate model and the initial access broker market. Hacktivists run for the message, with less sophistication and more visibility. Insiders run for grievance, and the insider remains the most damaging variant because the access is already legitimate and the alerts never fire. The portfolio is not new in 2026, but the supply chain has matured, and the initial access broker has become the upstream of the majority of ransomware incidents. CrowdStrike, Mandiant, and Microsoft all published the same data point in 2025: roughly 75 percent of ransomware intrusions started with brokered access.
What a penetration testing engagement actually is
A penetration testing engagement runs through three pieces, in the order the auditor will check them. The rules of engagement document, with the scope, the timing, the allowed methods, the reporting cadence, and the emergency contact for when the test accidentally hits a production system. Without a signed RoE, the engagement collapses and the tester is operating without consent. Then the testing itself, the technical work of finding and exploiting the vulnerabilities within the scope, and the work looks identical to what a real attacker would do. Then the report, the findings, the severity rating using CVSS or a comparable framework, the impact statement in business terms, the remediation steps the engineering team can actually run. A good pen test report sits as the only security deliverable the procurement lead reads in full.
When each one earns its place
The penetration testing engagement is the right answer for the predictable cadence. Quarterly, annual, or aligned to a major release, scoped to the crown jewel systems, performed by a qualified firm (NCC, Bishop Fox, Trail of Bits, or the internal red team for the larger shops). It is what the auditor asks about, what the SOC 2 examiner looks for, what the procurement questionnaire at the enterprise customer is going to ask. Skip it and the procurement team cannot close the deal.
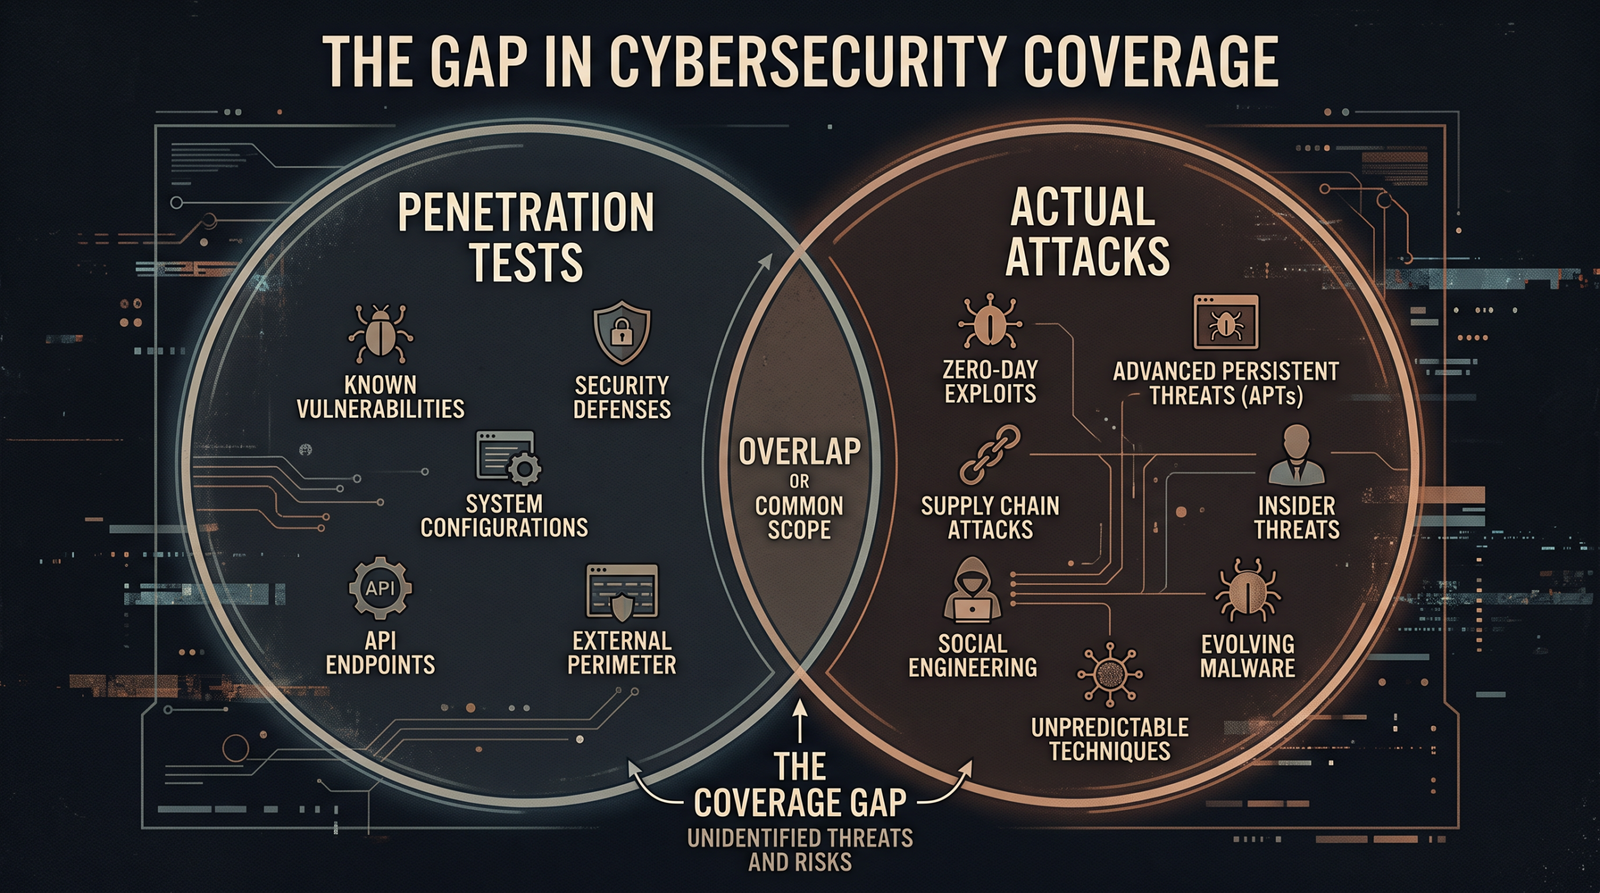
The bug bounty sits as the right answer for the long tail. HackerOne, Bugcrowd, Intigriti all run programmes that put a price on the unexpected, and the price scales with the severity. Microsoft, Google, and Apple have all shipped fixes that started as a bounty report. The bug bounty catches the vulnerability the pen test missed, the pen test catches the bug bounty hole. They are not substitutes.
The red team engagement is the right answer for the question the executive is asking. Can we detect the breach in progress. Can we contain the lateral movement. Can we recover in a time the business will tolerate. The red team assumes the perimeter has been breached and tests the back half, which is the half most programmes do not exercise. Mandiant and the larger consultancies run these as multi week engagements, with a defined objective and a rules of engagement, and the report tells the board whether the detection and response programme is real or theatre.
The bottom line
The craft is the same. The motivation and the consent are what separate the two. Run the pen test for the predictable cadence, the bug bounty for the long tail, the red team for the question the board is asking. Treat the penetration testing engagement as a checkbox and the auditor will know, the regulator will know, and the customer will know.
Sources & Further Reading
All claims in this article are sourced from primary documentation, vendor advisories, and reputable security researchers.
Spotted an error? Email the editor. Corrections are issued with a visible correction note.
Editorial standards. Every article on humanrequired.org is reviewed by a human editor before publication. AI may assist with drafting or research; final editorial control is human. Read the full standards.